Least Privilege at the Group Level
Lifecycle & Access Governance — Pillar 2

Group Automation

Faster deployment.

Rule-Based Group & Distribution-List Governance That Runs Itself
Eliminates manual group management by enforcing membership from your authoritative HR data automatically.

  • Groups and distribution lists follow authoritative HR data automatically as roles change.
  • Validate any rule against live data before enabling it — no surprises.
  • Most customers go live in days to weeks.
Trust It
SOC 2 Type 2 — Avatier compliance attestation
ISO/IEC 27001 — Avatier compliance attestation
PCI DSS v4.0.1 — Avatier compliance attestation
GDPR — Avatier compliance attestation
HIPAA — Avatier compliance attestation
HITECH — Avatier compliance attestation
NIST 800 Series — Avatier compliance attestation
NIST Cybersecurity Framework — Avatier compliance attestation
CISA Secure-by-Design — Avatier compliance attestation
CSA STAR Level 1 — Avatier compliance attestation
CSA STAR Level 2 — Avatier compliance attestation
CSA STAR AI Level 1 — Avatier compliance attestation
CSA AI Trustworthy Pledge — Avatier compliance attestation
FERPA — Avatier compliance attestation
FICAM — Avatier compliance attestation
VPAT — Avatier compliance attestation
WCAG 2.2 AA — Avatier compliance attestation
U.S. Air Force logo
U.S. Army logo
Bayer logo
BBC logo
Broward County logo
Build-A-Bear logo
The Cosmopolitan logo
DHL logo
Emerson logo
ESPN logo
Fox News logo
GSA logo
Humana logo
ING logo
Lockheed Martin logo
Marriott logo
MillerCoors logo
NASA logo
Nordstrom logo
Oscar Mayer logo
Pfizer logo
Rockwell Collins logo
SC Johnson logo
Sprint Canada logo
Starbucks logo
Steak 'n Shake logo
USA Today logo
Welch's logo
Vail Resorts logo
Visa logo
Volkswagen logo
Zep logo

Protecting the world’s workforce since 1997 • Over 15 Million Licenses Sold

Why It Matters

Group Membership Is Where Access Quietly Goes Wrong.

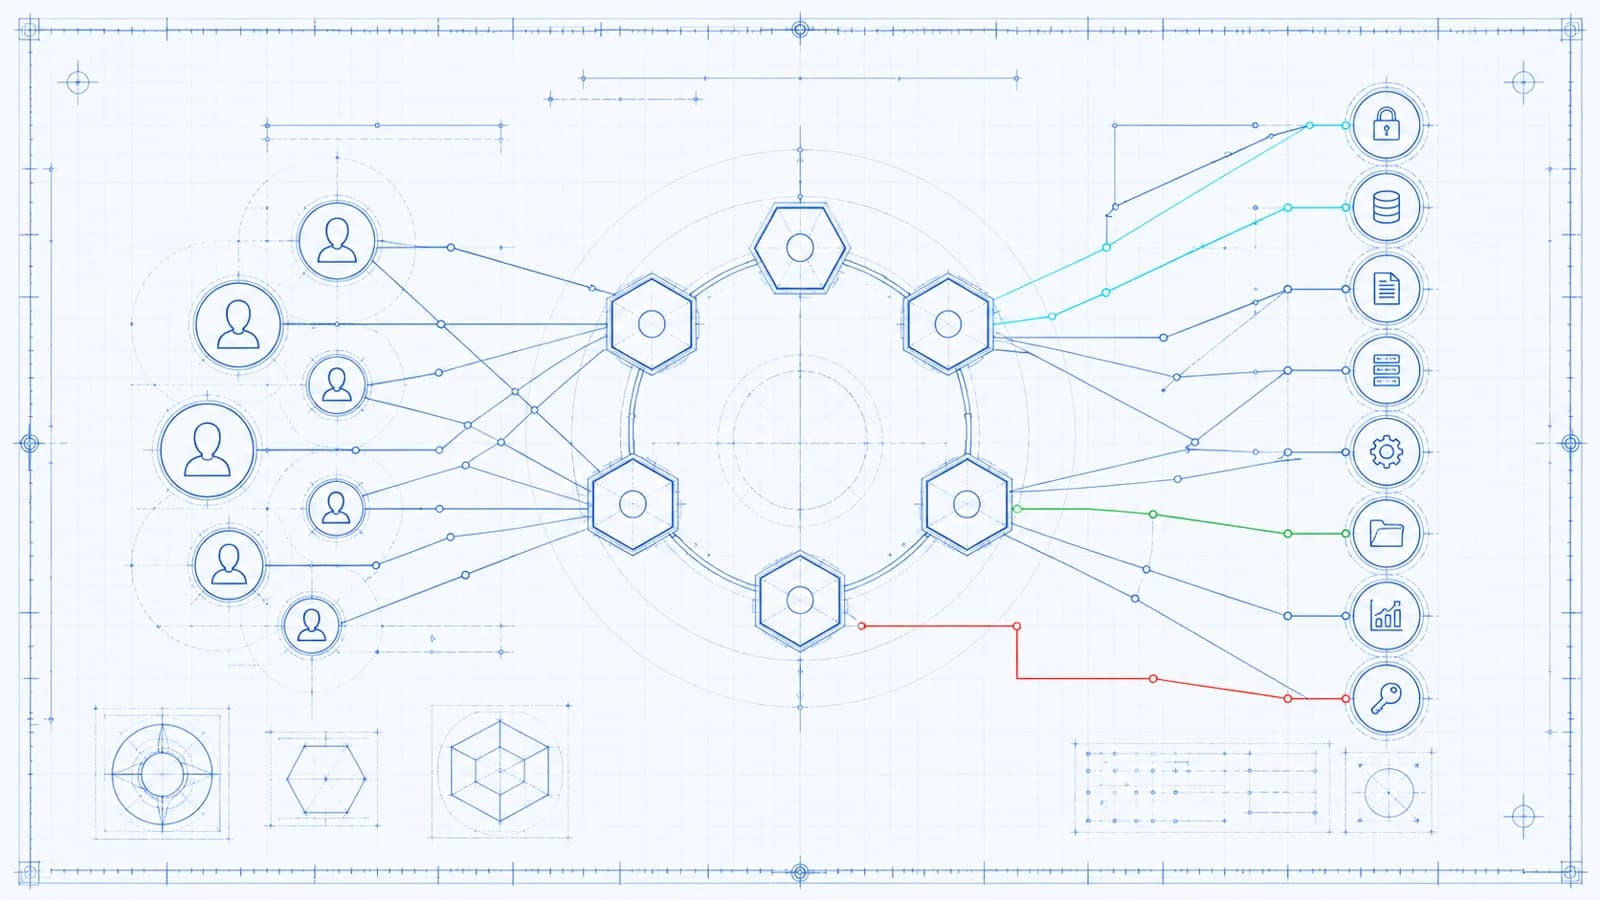
Manual group and distribution-list management is slow, error-prone, and impossible to audit at scale — and stale, over-permissioned groups are exactly how privilege creep and insider risk take hold.

Policy-enforced group automation
01

Avatier replaces manual administration with rule-based, policy-enforced group automation that keeps every security group and email distribution list continuously accurate, secure by design.

Stale, over-permissioned groups
02

Without automated enforcement, there is no reliable way to prove who belongs in a group — or to keep them out.

Authoritative HR attributes
03

By driving membership directly from authoritative HR attributes — title, department, location, and manager — Avatier places users in exactly the right groups the moment they are hired, moved, or termed, and removes them from the ones they should no longer be in.

Least privilege enforced automatically
04

For CISOs, that means least privilege enforced automatically, continuous audit evidence, and no unauthorized members hiding in privileged groups.

Daily, Weekly, or Monthly

Least Privilege Without IT Effort

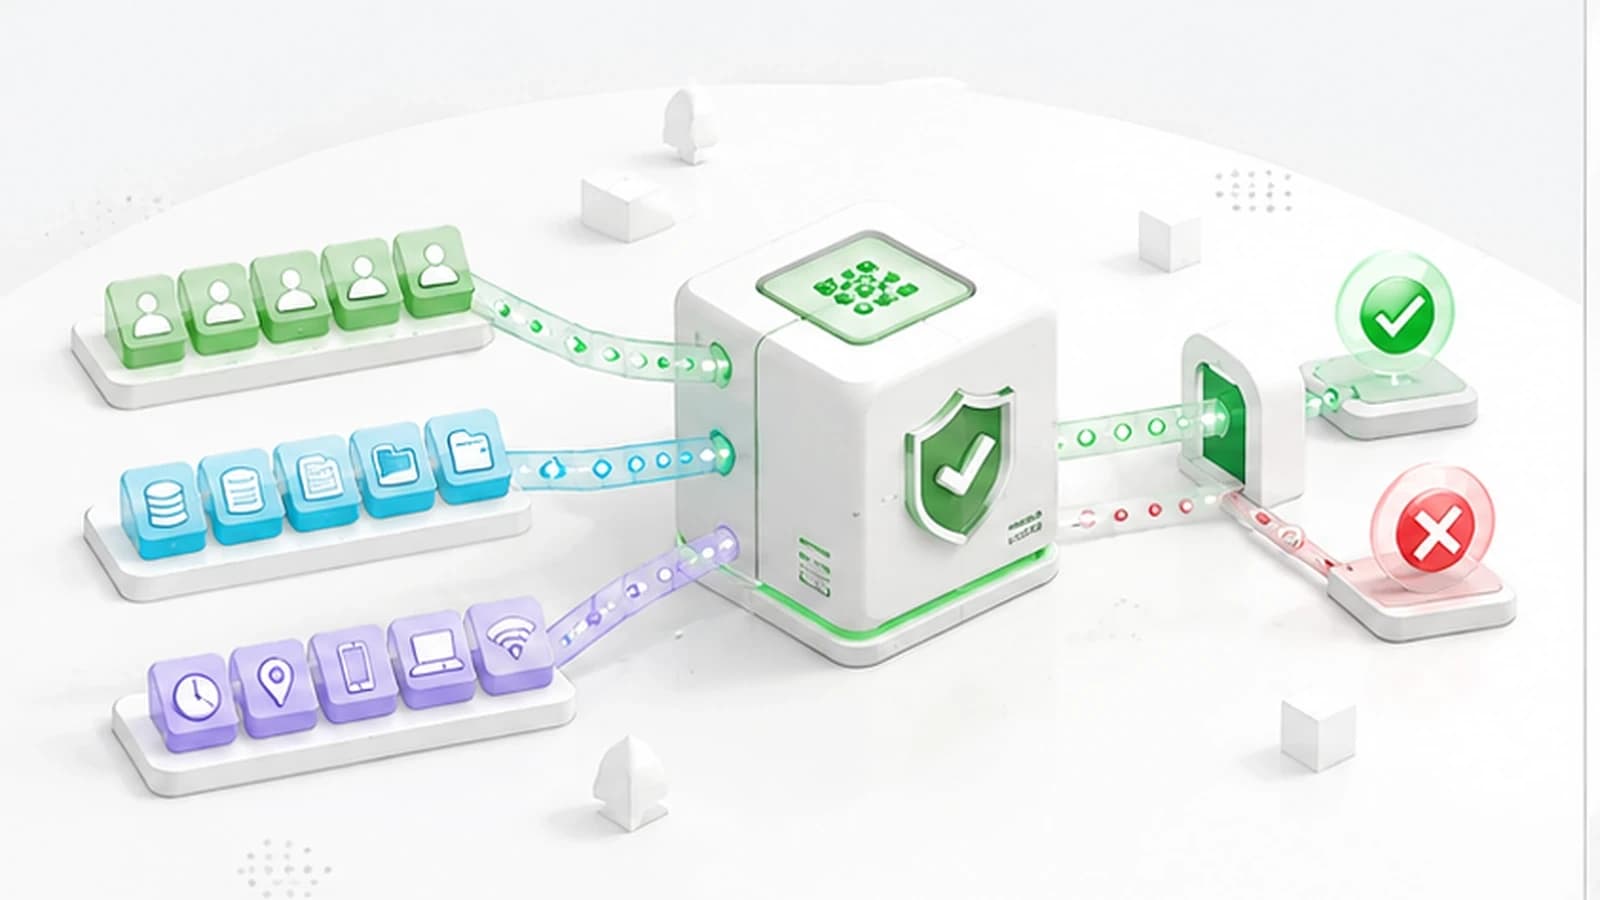
A wizard-driven rules engine lets business owners define membership by job attributes with no scripting. Avatier enforces those rules on the schedule you choose — daily, weekly, or monthly — continuously reconciling security groups and email distribution lists. You can test any rule before it goes live, handle exceptions with controlled manual overrides, and every change is captured for audit.

  1. 1

    No-Code Rules Engine

    • Define membership by job attributes
    • No scripting and no PowerShell
  2. 2

    Scheduled Enforcement

    • Daily, weekly, or monthly
    • Continuously reconciling security groups and email distribution lists
  3. 3

    Test-Before-Production

    • Test any rule before it goes live
    • See exactly who will be added or removed
  4. 4

    Exception Handling

    • Controlled manual overrides
  5. 5

    Patent-Pending Continuous Governance™

    • Flags unauthorized members and membership drift
    • Removes access that no longer fits
    • Restores what a user's role requires

Continuous monitoring flags unauthorized members and membership drift the moment they appear. Avatier's patent-pending Continuous Governance™ automatically removes access that no longer fits and restores what a user's role requires — enforcing least privilege without IT effort.

The Business Imperative

Stopping Access Creep and Group Sprawl

A single over-permissioned group can hand an attacker the keys to your network. When ransomware crews land a foothold, they look for one thing first: broad, poorly governed group memberships that let them move laterally and escalate to domain-wide control.

Manual group management guarantees this exposure. Memberships are added for a project and never removed, employees change roles but keep old group access, and privileged groups quietly accumulate members no one is reviewing. Without automated enforcement, there is no reliable way to prove who belongs in a group — or to keep them out.

Root CauseSolution
Membership CreepUsers keep old group access after transfers and projects end, accumulating standing privilege.HR-Driven EnforcementMembership is derived from live HR attributes, so access is added and removed automatically as roles change.
Unwatched Privileged GroupsNo automated process reviews who belongs in high-privilege security groups.Unauthorized-Member DetectionContinuous monitoring flags and removes members who don't match policy, with real-time alerts.
Manual, Unauditable ChangesAd-hoc group edits leave no reliable trail for auditors.Patent-Pending Continuous Governance™Every membership change is policy-enforced and logged, with automatic reconciliation to each user's current role.

Manual processes and disconnected directories create immense risk. Avatier Group Automation eliminates it by enforcing least privilege at the group level — continuously, automatically, and with full audit evidence.

Featured Capabilities

Least Privilege Enforced by Default, with Zero Group Sprawl

No-Code Rules Engine

Business owners define group membership by job attributes through a guided wizard — no scripting and no PowerShell. Test any rule against production data before you enable it, so you see exactly who will be added or removed before a single change is made.

Patent-Pending Continuous Governance™

Avatier's patent-pending Continuous Governance™ continuously reconciles every group — removing unauthorized members, restoring access aligned to each user's role, and alerting on drift the moment it appears. The result is least privilege enforced by default, with zero group sprawl.

Avatier Identity Anywhere 2027™ Preview

Build with the AI You Choose

Use the AI Assistant Tools You Already Love with Group Automation via Avatier's MCP

Premium personalization with zero consultant waste. Spin up an agent that requests access, checks entitlements, or pulls identity analytics—with Claude Code, OpenAI Codex, GitHub Copilot, or any MCP client.

Build with
  • Claude Code
  • OpenAI Codex
  • GitHub Copilot

MCP-Native Identity. Every Experience.

Voice, chat, or any API—identity shows up in

  • Web
  • Mobile
  • Microsoft Teams
  • Outlook
  • Chat
  • Voice
  • Phone
  • APIs
  • MCP-Compatible AI

One platform. Every identity experience secured.

Claude Code, OpenAI Codex, GitHub Copilot, Microsoft Teams and Outlook are trademarks of their respective owners. No partnership with or endorsement by any third party is implied.

Outcomes by Role

The Business Value of Group Automation Mapped to Who's Buying

Avatier Group Automation eliminates it by enforcing least privilege at the group level — continuously, automatically, and with full audit evidence.

Enterprise Trust

Is Every Change Auditable?

Yes. Every membership change is policy-enforced and logged with immutable audit trails, giving you continuous evidence for SOC 2, ISO 27001, NIST, SOX, HIPAA, and GDPR.

Certified

Independently audited

  • SOC 2 Type II
  • ISO 27001

Supports Compliance Evidence

Requirements and evidence needs

  • NIST
  • SOX
  • HIPAA
  • GDPR

Compliance-Ready Audit Trails

Continuous audit evidence

  • Every membership change is logged and policy-enforced for SOC 2, ISO 27001, NIST, SOX, and more.
  • Every change is logged for SOC 2, ISO 27001, NIST, and SOX evidence.

Integrations

One Unified Integration. Directories, HR & 70+ Systems.

Avatier enforces group membership from your authoritative sources through a single unified integration — no point-to-point connectors to build or maintain, and no scripts to break when a vendor changes an API.

  • Active Directory
  • Entra ID
  • Google Workspace
  • LDAP
  • Workday
  • SAP SuccessFactors
  • Oracle HCM
  • ADP
  • UKG
  • BambooHR

Key Advantages & Benefits

Designed for Speed, Security, and Simplicity

Avatier delivers a modern, AI-driven identity and workforce automation platform designed for speed, security, and simplicity.

AdvantageKey BenefitWhy It Matters
No-Code Rules EngineFaster DeploymentWizard-driven, attribute-based rules eliminate scripting and cut rollout time from months to days.
HR-Driven MembershipZero-Touch Group ManagementGroups and distribution lists follow authoritative HR data automatically as roles change.
Scheduled EnforcementAlways-Accurate GroupsDaily, weekly, or monthly reconciliation keeps every group continuously correct.
Unauthorized-Member DetectionReduced RiskContinuous monitoring flags and removes members who don't match policy, with real-time alerts.
Patent-Pending Continuous Governance™Always-Right AccessAutomatic role reconciliation removes or restores membership to match each user's role, eliminating access creep.
Test-Before-ProductionSafe ChangesValidate any rule against live data before enabling it — no surprises.
Distribution-List AutomationHigher ProductivityEmail distribution lists are built and maintained automatically from HR attributes.
Compliance-Ready Audit TrailsAudit ConfidenceEvery membership change is logged and policy-enforced for SOC 2, ISO 27001, NIST, SOX, and more.
Docker DeploymentDeploy AnywhereRuns on-premise, in the cloud, or fully hosted with isolation by design.

Top Use Cases

Every Membership Change Is Policy-Enforced and Logged

  • Security Group Automation

    Membership for AD and Entra ID security groups is enforced from authoritative attributes.

  • Email Distribution List Automation

    Distribution lists are built and maintained automatically — no manual edits.

  • HR-Driven Membership

    Title, department, location, and manager drive attribute-based group assignment.

  • New-Hire Group Assignment

    New employees land in exactly the right groups on day one.

  • Transfer / Role-Change Re-Grouping

    Role changes add new group access and remove what no longer fits.

  • Offboarding Group Cleanup

    Departures are removed from every group instantly, eliminating stale access.

  • Unauthorized-Member Detection

    Continuous monitoring flags and removes members who don't match policy.

  • Nested & Dynamic Group Governance

    Complex nested and dynamic group structures stay accurate automatically.

  • Contractor, Supplier & Partner Groups

    Non-employee populations are governed by the same attribute-based rules.

  • Scheduled Enforcement

    Rules run on a daily, weekly, or monthly cadence you control.

  • Test Rule Before Production

    Preview exactly who a rule will add or remove before enabling it.

  • Exception Handling

    Controlled manual overrides cover the edge cases policy can't.

  • Application Access via Groups

    Group-based application entitlements stay aligned to role.

  • Compliance-Ready Audit Reporting

    Every change is logged for SOC 2, ISO 27001, NIST, and SOX evidence.

  • Continuous Governance™ Reconciliation

    Automatic role reconciliation keeps membership matched to each user's current role.

  • Separation-of-Duties Enforcement

    Rules prevent toxic combinations of group access from ever accumulating.

Perfect For These Scenarios

Critical Value and Rapid ROI

Avatier Group Automation delivers critical value and rapid ROI for organizations facing these common challenges.

Large Active Directory Estates
Organizations with sprawling AD/Entra ID groups that are impossible to govern by hand.
Regulated Industries
Organizations requiring SOC 2, ISO 27001, NIST, SOX, HIPAA, or GDPR access evidence.
M&A or Reorganization
Businesses where roles and structures change fast and group access must keep up.
HR-Driven Enterprises
Companies seeking to govern group membership from a single source of truth.
Previous Audit Findings
Organizations remediating over-permissioned groups, stale membership, or access creep.

Rollout

How Fast Can We Go Live?

Avatier deploys as Docker containers on-premise, in the cloud, or fully hosted, with a private cloud instance and isolation by design.

How fast
Most customers go live in days to weeks.
What's required
Point-and-click configuration.
Who owns rollout
A dedicated onboarding team.
User experience
Business owners define and manage membership without scripting.
Global reach

Identity Verification in 34 Languages

34 languages, 24 x 365 always-on identity verification.

Arabic flagArabicSupported
Arabic League (Egyptian) flagArabic League (Egyptian)Supported
Bengali flagBengaliSupported
Catalan flagCatalanSupported
Chinese (Simplified) flagChinese (Simplified)Supported
Chinese (Traditional) flagChinese (Traditional)Supported
Czech flagCzechSupported
Danish flagDanishSupported
Dutch flagDutchSupported
English flagEnglishCurrent Site
Finnish flagFinnishSupported
French flagFrenchSupported
French (Canadian) flagFrench (Canadian)Supported
German flagGermanSupported
Greek flagGreekSupported
Hindi flagHindiSupported
Hungarian flagHungarianSupported
Indonesian flagIndonesianSupported
Italian flagItalianSupported
Japanese flagJapaneseSupported
Korean flagKoreanSupported
Norwegian flagNorwegianSupported
Polish flagPolishSupported
Portuguese flagPortugueseSupported
Portuguese (Brazil) flagPortuguese (Brazil)Supported
Russian flagRussianSupported
Slovak flagSlovakSupported
Spanish flagSpanishSupported
Spanish (Americas) flagSpanish (Americas)Supported
Swahili flagSwahiliSupported
Swedish flagSwedishSupported
Thai flagThaiSupported
Turkish flagTurkishSupported
Urdu flagUrduSupported
Group Automation FAQs

Frequently Asked Questions

Answers for business owners, security and compliance, and IT.

How membership is decided, tested and kept current

Recognized on Gartner Peer Insights

4.4

Based on 14 verified customer reviewsIdentity Governance and Administration

Read the reviews on Gartner Peer Insights

Governed Groups, Enforced Automatically

You've Automated the Accounts — Now Govern the Groups.

Automation can solve most IT tasks — but group membership remains a critical, manual risk that quietly drives access creep and insider exposure. Avatier Group Automation enforces the right membership everywhere, transforming authoritative HR data into the single source of truth for group access. It turns your directories into a governed, least-privilege environment where every user has exactly the group access their role requires — and none they don't.

This is how you close the access-creep gap at the group level: by automating governance continuously, from hire to retire.

Continuous Governance™, Password Firewall™, and Identity Anywhere™ are trademarks of Avatier Corporation. Patent pending.